COWMODSКаталог модов

Login+

Best new gen auth plugin to your servers !

Автор: Critic2,3 тыс.2обновлён 4 сент. 2026 г.
Механики игрыУправлениеУтилиты

Описание

🔐 Login+

Register once, stay protected forever. Login+ is a modern authentication plugin for offline-mode servers — passwords, sessions, free 2FA and full account protection in one jar for Spigot/Paper 1.8.8 → 1.21+.

Written in Kotlin, runs fully server side, so every client and every client version is supported. No mods, no datapacks, no paid services — drop the jar in, restart, done.

🛡️ Your players' passwords are protected with Argon2id — winner of the Password Hashing Competition and OWASP's #1 recommendation. Its memory-hard design makes large-scale GPU brute-force attacks impractical. Passwords are never stored as readable text — not even the server owner can recover them.


✨ Features

  • 🔑 Argon2id password hashing — the strongest password protection available today, with OWASP-baseline defaults you can raise in the config
  • ⏱️ Sessions — reconnect within 15 minutes (configurable) from the same IP and skip the login. Survives server restarts
  • 📱 Free 2FA — three flavours:
    • Google Authenticator (TOTP) — works 100% offline, the QR code is rendered on an in-game map item for easy scanning
    • Discord — your own bot DMs the login code
    • Telegram — your own bot sends the login code
  • 🚨 Security alerts — players with Discord/Telegram linked get warned about new-IP logins, brute-force attempts and password changes — even while offline
  • 🙈 Console password shield — /login and /register are intercepted so passwords never appear in the console or log files
  • 🧱 Full freeze before login — no moving, chatting, commands, damage, inventory or item pickup; optional blindness and spawn teleport that hides base coordinates from stream snipers
  • 🤖 Anti-bot & brute-force protection — per-player attempt limits, per-IP lockouts, join-flood lockdown, username regex filter, per-IP account limits
  • 🎭 Anti-impersonation — kicks NoTcH if the account was registered as Notch, blocks duplicate names, optional UUID checks
  • 💎 Premium mode — /premium lets verified Mojang accounts skip the password (only when the connection can actually be verified — Login+ never pretends)
  • 📧 E-mail recovery — forgot the password? A one-time code is mailed via your own SMTP mailbox. 2FA still applies after recovery
  • 🌍 Country filter — whitelist or blacklist joins by country
  • 🌐 Proxy ready — works behind Velocity, BungeeCord and Waterfall; with shared MySQL, sessions carry across backend servers (no re-login when switching). Login+ checks your forwarding setup on startup and prints hints
  • 🔊 Sound feedback — level-up chime on success, buzzer on wrong password (cross-version safe)
  • 🗄️ SQLite out of the box, MySQL for networks — with automatic scheduled backups
  • 🌏 Fully translatable — clean English and Russian message files included

⚙️ Commands & Permissions

CommandPermissionShort Description
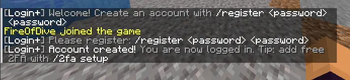
/register <pass> <pass>loginplus.player.registerCreate an account
/login <pass> (alias /l)loginplus.player.loginLog in
/logoutloginplus.player.logoutLog out and lock the account
/changepassword <old> <new>loginplus.player.changepasswordChange password
/unregister <pass>loginplus.player.unregisterDelete own account
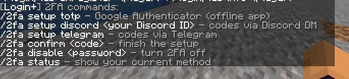
/2fa setup <totp|discord|telegram>loginplus.player.2faEnable two-factor auth
/2fa <code>loginplus.player.2faEnter the code during login
/email set <address>loginplus.player.emailBind a recovery e-mail
/email recoveryloginplus.player.emailRecover a forgotten password
/premium / /freemiumloginplus.player.premiumToggle Mojang auto-login
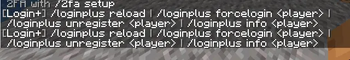
/loginplus <reload|forcelogin|unregister|info>loginplus.adminAdmin commands

All player permissions default to true; admin commands default to OP.


🚀 Quick Start

  1. Drop the jar into /plugins and restart the server.
  2. Players run /register <password> <password>, then /login <password> next time.
  3. (Optional) Enable free 2FA, e-mail recovery and more in config.yml — every option is documented right in the file.

Setting up the 2FA bots (both 100% free)

  • Telegram: message @BotFather → /newbot → copy the token into config.yml. Players run /2fa setup telegram.
  • Discord: discord.com/developers/applications → New Application → Bot → copy the token into config.yml. Players run /2fa setup discord <their user ID>.
  • Google Authenticator: nothing to set up — players just run /2fa setup totp and scan the QR map. Works offline.

🌐 Running behind Velocity / BungeeCord / Waterfall

Login+ runs on your backend (Spigot/Paper) servers and fully supports proxy networks:

  1. Enable IP forwarding on both sides (proxy and backend).
  2. For multi-server networks set storage.type: MYSQL and point every backend at the same database — players switching servers stay logged in seamlessly.
  3. Firewall the backend ports so players can only connect through the proxy.

Login+ verifies the forwarding configuration on startup and prints console hints if something looks wrong.


💡 Some Advice

  • Login+ is built for offline-mode servers — for example, the backend servers behind a Velocity, BungeeCord or Waterfall proxy, where Minecraft's own account verification is turned off and a login plugin is what keeps every account secure. Pure online-mode (premium) servers are already verified by Mojang, so they don't need a login plugin.
  • Avoid /reload; restart the server instead.
  • Honest security note: /premium only activates when Mojang really verified the connection (online-mode server or online-mode proxy with modern forwarding). On a plain offline-mode server there is nothing to verify, so it politely refuses instead of pretending to be secure.

Галерея
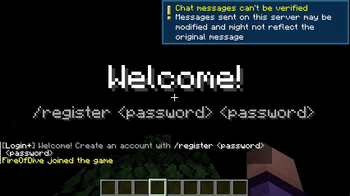
RegistrationSuccesfull Log-inAll Commands2FA Commands

Последние версии

Все версии →
release

Login+ 1.0.2 ( UPDATE ) Major Bug fixing !

1.0.2
4 сент. 2026 г.1,2 тыс.Minecraft: 1.8, 1.8.1, 1.8.2, 1.8.3, 1.8.4, 1.8.5, 1.8.6, 1.8.7, 1.8.8, 1.8.9, 1.9, 1.9.1, 1.9.2, 1.9.3, 1.9.4, 1.10, 1.10.1, 1.10.2, 1.11, 1.11.1, 1.11.2, 1.12, 1.12.1, 1.12.2, 1.13, 1.13.1, 1.13.2, 1.14, 1.14.1, 1.14.2, 1.14.3, 1.14.4, 1.15, 1.15.1, 1.15.2, 1.16, 1.16.1, 1.16.2, 1.16.3, 1.16.4, 1.16.5, 1.17, 1.17.1, 1.18, 1.18.1, 1.18.2, 1.19, 1.19.1, 1.19.2, 1.19.3, 1.19.4, 1.20, 1.20.1, 1.20.2, 1.20.3, 1.20.4, 1.20.5, 1.20.6, 1.21, 1.21.1, 1.21.2, 1.21.3, 1.21.4, 1.21.5, 1.21.6, 1.21.7, 1.21.8, 1.21.9, 1.21.10, 1.21.11, 26.1, 26.1.1, 26.1.2, 26.2bukkit, paper, purpur, spigot, velocity
Скачать
Что нового
> **⚠️ This update is required.** Version 1.0.1 and below contain a critical login bypass that lets an attacker join a registered account without its password. If your server uses premium mode, update now — leaving an older version running puts every account on your server at risk. Hello everyone! Login+ **1.0.2** fixes that critical login bug, adds Velocity support and makes the plugin easier to set up. ### Security - **Fixed a critical authentication flaw in premium mode.** Under certain conditions a registered account could be joined without entering its password. Updating is a drop-in — no config or database changes are required, so there is no reason to stay on an old version. ### Added - **Velocity support.** Login+ now runs on the proxy as well, so players authenticate once at the entrance and stay logged in on every backend server. The plugin must be installed **on the proxy and on every backend server** behind it. - **Login MOTD.** A welcome message of your own is sent the moment a player is authenticated. - **Login titles.** A title and subtitle appear on screen after a successful login — text, colors and timings are all yours to set. ### Changed - **Simpler customisation.** The new MOTD and titles are edited in one place in plain text with the usual color codes, and can be disabled completely. - **Cleaner config layout.** Options are grouped by feature and much easier to find. Your existing `config.yml` is upgraded automatically on first start and all of your own values are kept. --- Updating from **1.0.1** is a drop-in: just replace the jar. The database and config upgrade themselves, and customized message files keep working.
release

Login+ 1.0.1 ( UPDATE ) Minor Fixes and New features !

1.0.1
11 июл. 2026 г.808Minecraft: 1.8, 1.8.1, 1.8.2, 1.8.3, 1.8.4, 1.8.5, 1.8.6, 1.8.7, 1.8.8, 1.8.9, 1.9, 1.9.1, 1.9.2, 1.9.3, 1.9.4, 1.10, 1.10.1, 1.10.2, 1.11, 1.11.1, 1.11.2, 1.12, 1.12.1, 1.12.2, 1.13, 1.13.1, 1.13.2, 1.14, 1.14.1, 1.14.2, 1.14.3, 1.14.4, 1.15, 1.15.1, 1.15.2, 1.16, 1.16.1, 1.16.2, 1.16.3, 1.16.4, 1.16.5, 1.17, 1.17.1, 1.18, 1.18.1, 1.18.2, 1.19, 1.19.1, 1.19.2, 1.19.3, 1.19.4, 1.20, 1.20.1, 1.20.2, 1.20.3, 1.20.4, 1.20.5, 1.20.6, 1.21, 1.21.1, 1.21.2, 1.21.3, 1.21.4, 1.21.5, 1.21.6, 1.21.7, 1.21.8, 1.21.9, 1.21.10, 1.21.11, 26.1, 26.1.1, 26.1.2, 26.2bukkit, paper, purpur, spigot
Скачать
Что нового
--- Hello everyone, today Login+ gets its first update — four new features and a big round of security hardening, fully translated into English and Russian! - Added one-time 2FA backup codes: enabling 2FA now gives you 8 single-use codes like XXXX-XXXX that log you in if you ever lose your authenticator, Discord or Telegram — check how many are left with /2fa status, generate a fresh set with /2fa backup <password>, and the account owner gets a security alert whenever one is used; only hashes are stored, so the codes can never be read back, not even by the server owner - Added account migration from other auth plugins through /loginplus import <authme|nlogin> [file], which imports names, registration dates, IPs and recovery e-mails from the AuthMe or nLogin database (SQLite); old password hashes keep working and are upgraded to Argon2id automatically at each player's first login, so players notice nothing at all - Added forced 2FA for staff: anyone with the new permission loginplus.require2fa (or every operator, with the new config option two-factor.require-for-staff.ops) is frozen after logging in until they finish /2fa setup — skipped automatically while no 2FA method is enabled, so a config mistake can never lock your team out - Added Telegram one-tap login approval — login requests now arrive with ✅ It's me / ❌ Not me buttons, one tap logs you in or kicks the attacker, and typing the 6-digit code still works as a fallback (new config option two-factor.telegram.one-tap-approve, on by default) - Improved the /loginplus help, which now lists one command per line with a short description instead of cramming everything into a single line, matching the /2fa and /email style - Fixed password checks in /changepassword, /unregister, /2fa disable and /email remove having no attempt limit, which let a stolen session brute-force the account password unnoticed and spam the server with heavy hash computations; three wrong passwords now lock these commands for a while and warn the account owner via Discord/Telegram - Fixed e-mail recovery codes being guessable by command spam — three wrong tries now invalidate the code and end the connection - Fixed the e-mail cooldown resetting when a player rejoins, which could be abused to flood someone's inbox with recovery mails; the cooldown is now tied to the account and survives relogging - Fixed /2fa resend having no cooldown, which allowed flooding a player's DMs with login codes — requesting a new code now has a 30-second cooldown - Fixed 2FA setup confirmation codes never expiring and accepting unlimited guesses; they now expire after 10 minutes and are dropped after three wrong attempts, and e-mail confirmation codes got the same three-attempt limit - Fixed e-mail recovery codes being guessable by command spam — three wrong tries now invalidate the code and end the connection - Fixed the e-mail cooldown resetting when a player rejoins, which could be abused to flood someone's inbox with recovery mails; the cooldown is now tied to the account and survives relogging - Fixed /2fa resend having no cooldown, which allowed flooding a player's DMs with login codes — requesting a new code now has a 30-second cooldown - Fixed 2FA setup confirmation codes never expiring and accepting unlimited guesses; they now expire after 10 minutes and are dropped after three wrong attempts, and e-mail confirmation codes got the same three-attempt limit Updating from 1.0.0 is a drop-in: just replace the jar — the database and config upgrade themselves, and customized message files keep working.
release

Login+ First Realese

1.0.0
10 июн. 2026 г.224Minecraft: 1.8, 1.8.1, 1.8.2, 1.8.3, 1.8.4, 1.8.5, 1.8.6, 1.8.7, 1.8.8, 1.8.9, 1.9, 1.9.1, 1.9.2, 1.9.3, 1.9.4, 1.10, 1.10.1, 1.10.2, 1.11, 1.11.1, 1.11.2, 1.12, 1.12.1, 1.12.2, 1.13, 1.13.1, 1.13.2, 1.14, 1.14.1, 1.14.2, 1.14.3, 1.14.4, 1.15, 1.15.1, 1.15.2, 1.16, 1.16.1, 1.16.2, 1.16.3, 1.16.4, 1.16.5, 1.17, 1.17.1, 1.18, 1.18.1, 1.18.2, 1.19, 1.19.1, 1.19.2, 1.19.3, 1.19.4, 1.20, 1.20.1, 1.20.2, 1.20.3, 1.20.4, 1.20.5, 1.20.6, 1.21, 1.21.1, 1.21.2, 1.21.3, 1.21.4, 1.21.5, 1.21.6, 1.21.7, 1.21.8, 1.21.9, 1.21.10, 1.21.11, 26.1, 26.1.1, 26.1.2bukkit, paper, purpur, spigot
Скачать
Что нового
Write the bugs here: https://discord.gg/BRVmQVNPQQ Support me: https://buymeacoffee.com/criticai